User Management
On this page
Every person who signs in to Primentra needs a user account. Accounts are created and managed in Settings › Access Management › Users.
Watch it in 3:36 — the three badges, an account created and given a role, an address refused because it already exists, and the last administrator refused a switch-off:
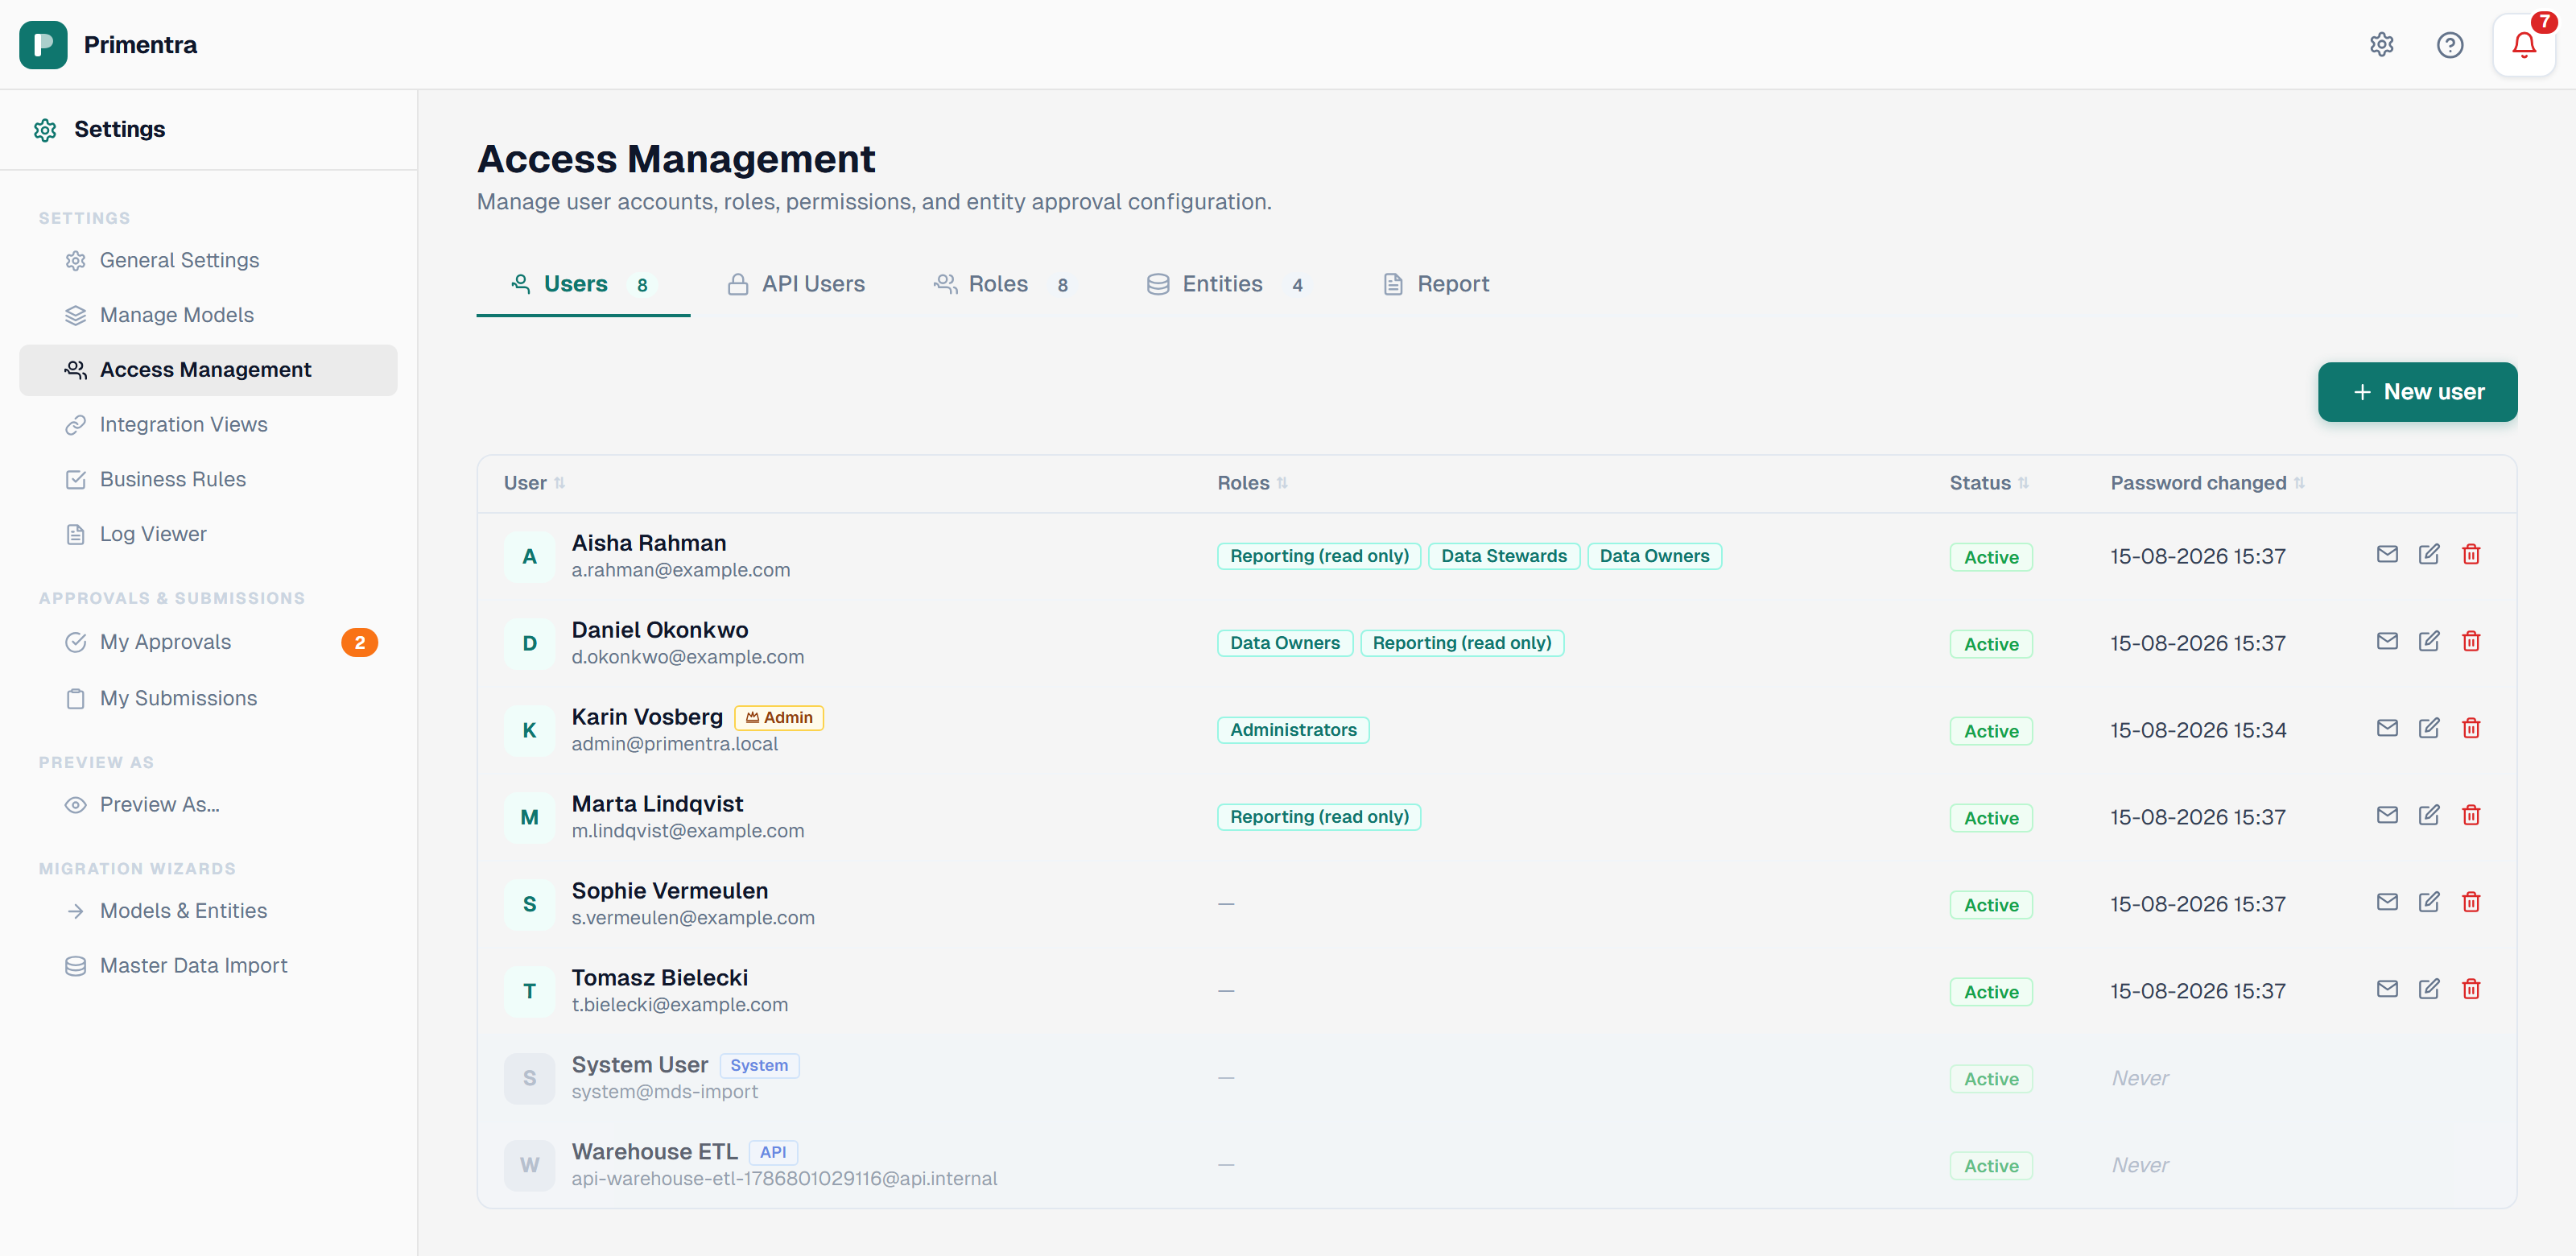
The user list
The list is a sortable table. Click any column header to cycle through ascending, descending, and unsorted.
| Column | Shows |
|---|---|
| User | Display name, email address, and badges |
| Roles | Every role the user belongs to |
| Status | Active or Inactive |
| Last sign-in | When the user last signed in, or Never |
Four badges can appear next to a name:
- Admin (crown) — the user belongs to a role with the Administrator flag
- AD user — the user is linked to an Active Directory account, see below. A user who is not linked has no badge
- System — Primentra's own account, see below
- API — an API service account, see below
Click a row to open the account. The action buttons on the right send the welcome email, edit the account, or delete it.
For an AD user, the welcome email says to choose Windows account on the sign-in screen and to type the Windows user name and password. It contains no Primentra password and no sign-in link.
Create a user
When Active Directory sign-in is on, New user starts with the choice Type of user: Primentra user or AD user. The steps below are for a Primentra user. For an AD user, see the next part.
- Click New user.
- Enter the Email. This is the login name and must be unique.
- Enter the Display Name. It appears in the settings menu and the audit log.
- Enter a Password, or click Generate for a random 16-character password. Use the eye icon to check it.
- Leave User must change password at next login ticked if the user must choose their own password.
- Leave Send welcome email ticked to mail the account details.
- Under Sign-in status, leave Enabled ticked.
- Tick the roles the user belongs to.
- Click Create user.
Create an AD user
The choice Type of user shows only while AD sign-in is on.
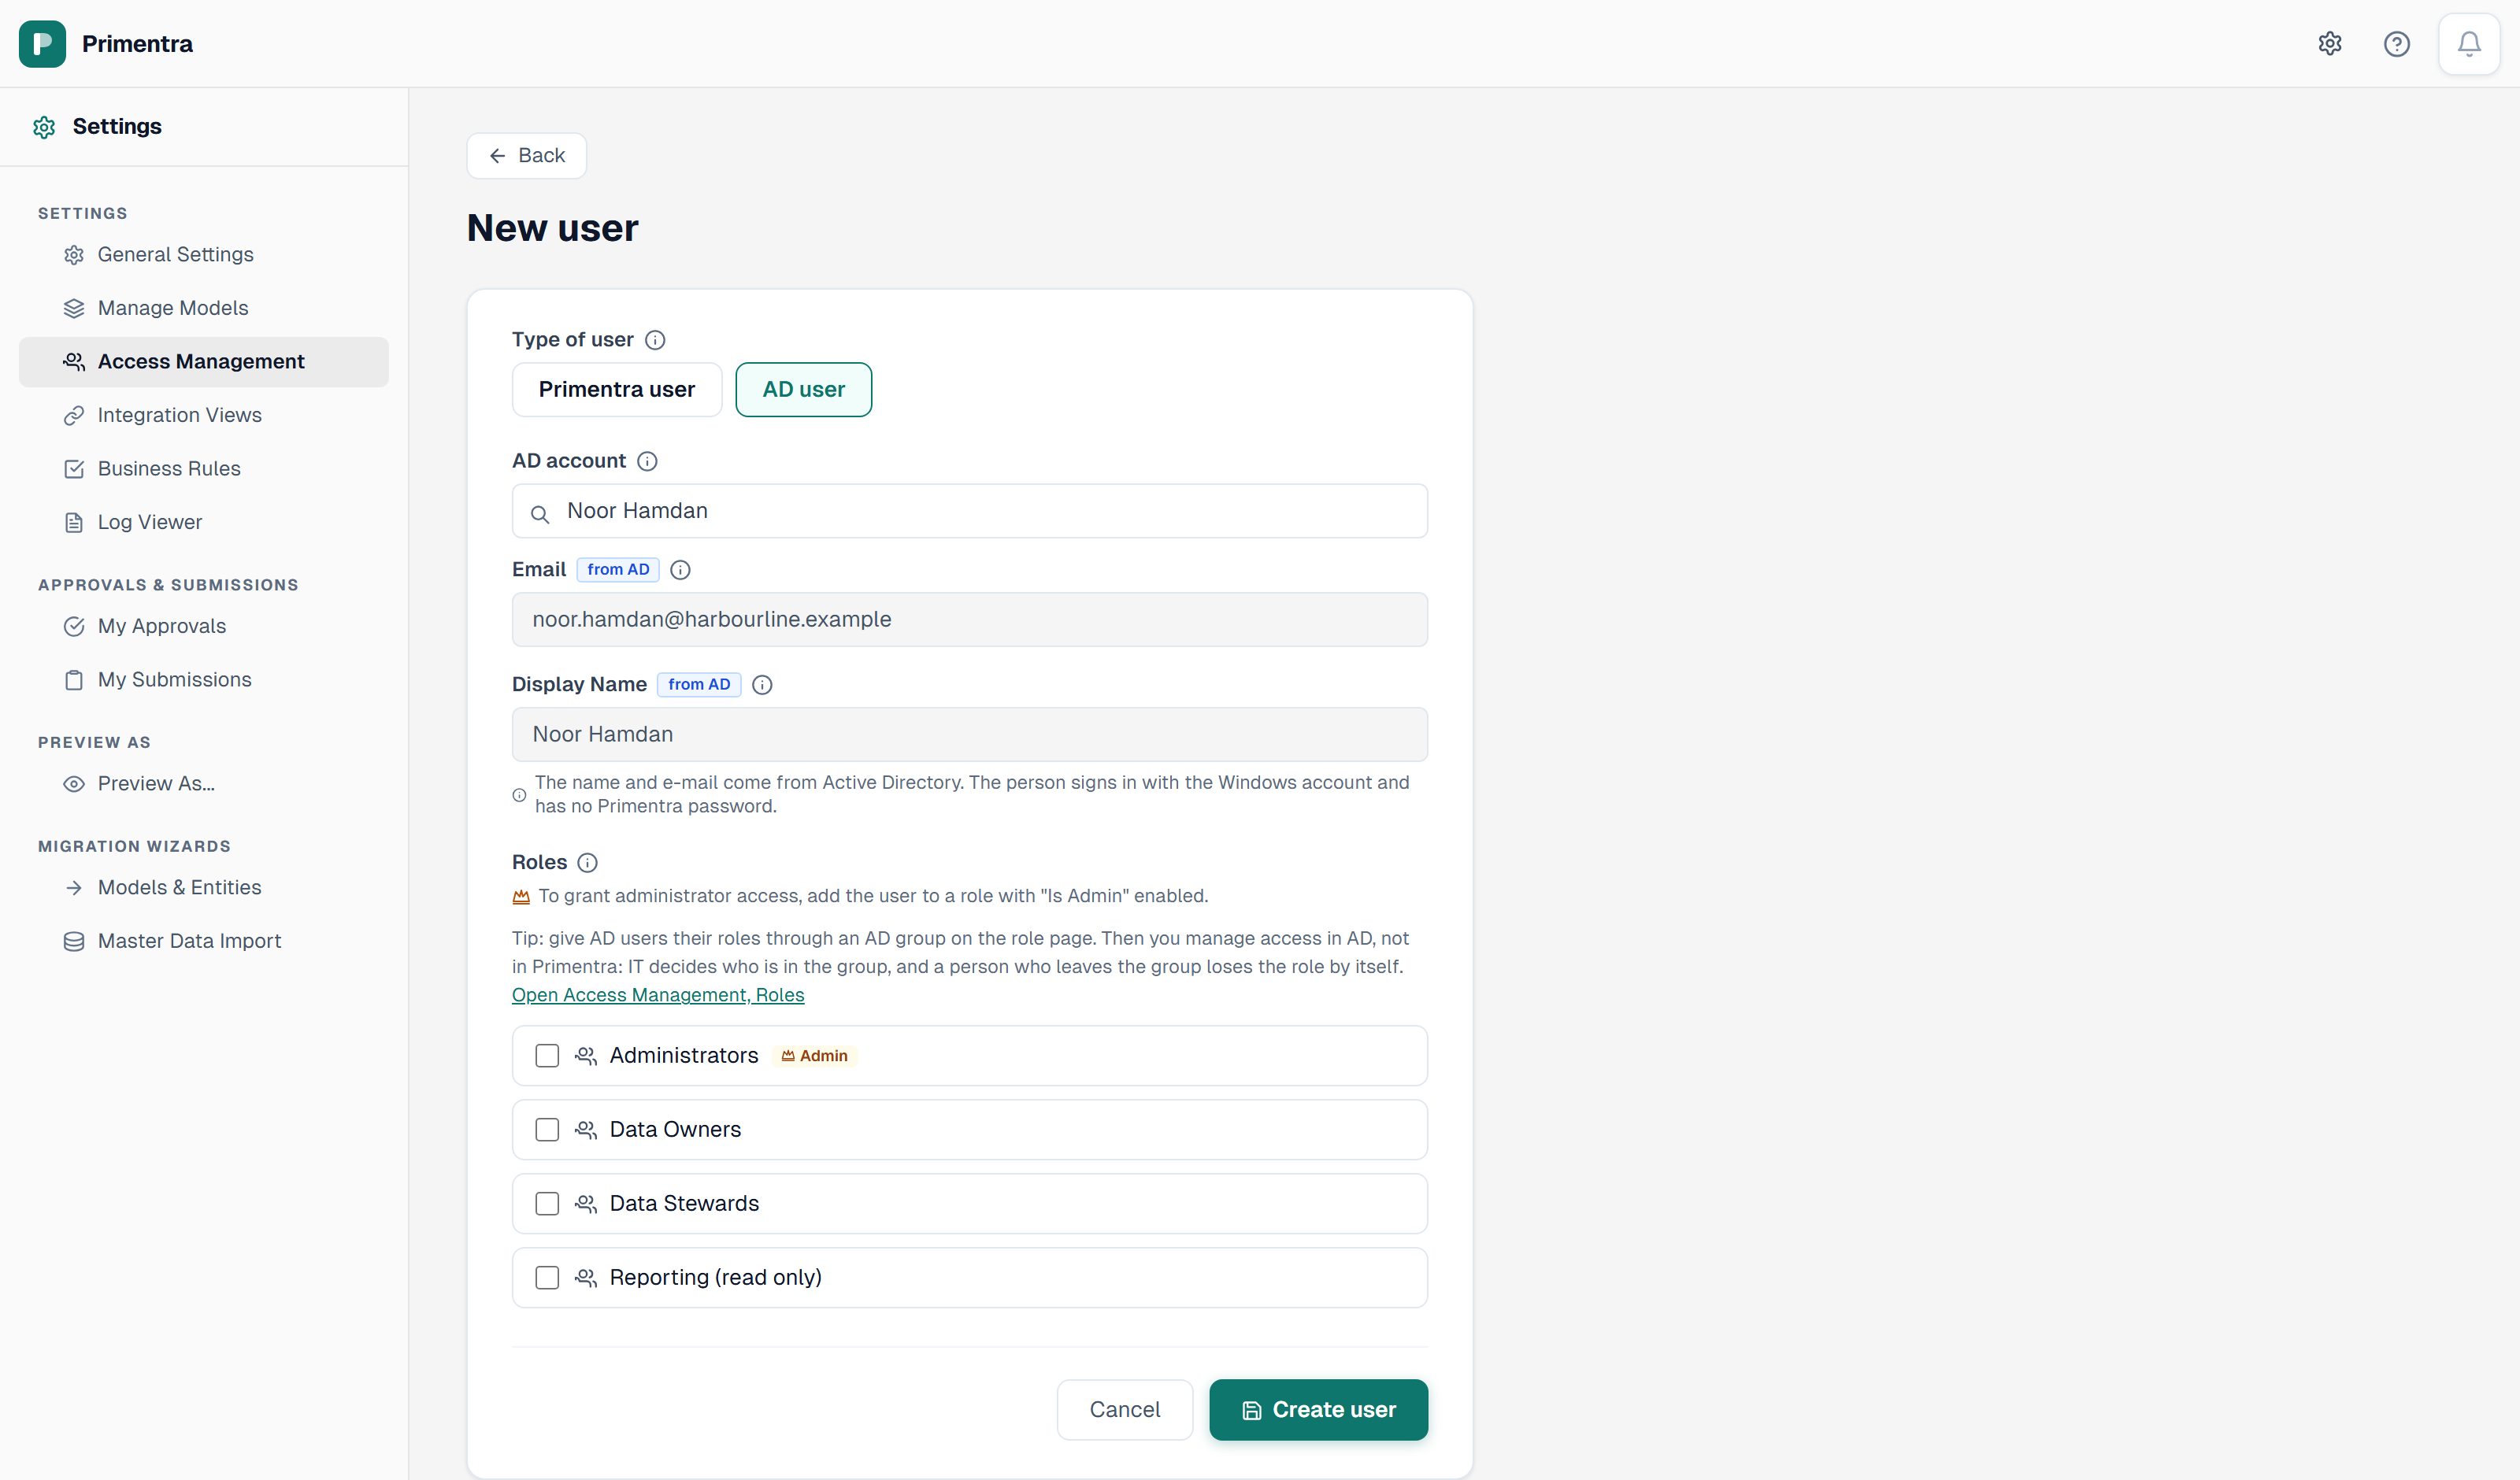
- Click New user and choose AD user.
- In the box AD account, type two or more letters of the person's name, user name or email. Pick the account.
- Check Email and Display Name. They come from AD, and you cannot edit them. When the account has no
mail, the marker email from UPN shows. - Tick the roles the user needs. A gray tip says that an AD group on the role page is better.
- Click Create user.
The user is linked to the AD account and has no Primentra password.
An account that already exists in Primentra shows Already in Primentra, with the link Open user. You cannot add it twice. An account that is disabled in AD shows disabled in Active Directory, and you cannot pick it. Primentra refuses the same accounts as Add user on a role page. A user that you add from a role page is the same kind of user: a linked user with the AD badge.
The welcome email
The welcome email is branded HTML. What it contains depends on the Must change password setting.
| Must change password | The email contains |
|---|---|
| On | A one-click sign-in link, valid 72 hours, single use. No password is included. |
| Off | The login name, the password, and a sign-in button. |
Both versions list the user's role memberships.
To send it again later, click the mail icon on the user's row. A resent email never contains a password, because passwords are not stored in readable form.
Sending is non-blocking. If the mail server is unavailable, the account is still created and a toast reports the failure.
Edit a user
Open the account and change any field. Leave the password box empty to keep the current password. Role changes apply as soon as you save.
The Password last changed date is shown in the Account panel and cannot be edited.
The Account panel
Beside the form, the page shows a read-only Account panel. It tells you where the user came from.
| Line | What it shows |
|---|---|
| Sign-in | Active Directory with the account and an Unlink button, or Primentra password with a Link to AD account button |
| Password last changed | The date, Never changed, or No Primentra password |
| Created | The date, and how: by an administrator, at the first Active Directory sign-in, from Active Directory, on the role page, from Active Directory, on New user, by a model import, by an MDS migration, or at the first Active Directory sign-in, from an MDS migration. Where it is known, it also says by whom |
| Last changed | The date and by whom. It says by Active Directory when a sign-in copied a new name or email |
| Last sign-in | The date, or Never, and the way: Primentra password, AD user name and password or Windows |
A value that Primentra did not record shows Not recorded. This applies to users created before this feature existed. Primentra does not guess. For an AD user, Email and Display Name are read-only and have a small from AD badge. Change them in AD, and Primentra copies them at the next sign-in.
Enabled and Locked out
The form has a Sign-in status box with two separate flags. Both block sign-in. Only an administrator can clear Enabled, but a lock also ends by itself.
| Flag | Set by | Cleared by | Effect |
|---|---|---|---|
| Enabled | An administrator | An administrator | When off, the user cannot sign in at all. Only an administrator can switch it on. |
| Locked out | Primentra, after five wrong passwords | The lock ends by itself after 30 minutes, when the user sets a new password with Forgot password?, or when an administrator clears it | The user cannot sign in with a Primentra password until it ends. It does not stop a Windows sign-in. |
The list shows one badge per state: Active, Disabled (Enabled is off) or Locked out. A user can be Disabled and Locked out at the same time. Point at a badge to read the tooltip.
To end a lock before the 30 minutes are up, open the account, untick Locked out and click Save. The user can sign in again and the failed-attempt counter goes back to zero. For a locked user the form shows Locked on [date] after five wrong passwords.
You cannot lock a user by hand: Locked out stays disabled unless the user is already locked. To block a user, clear Enabled.
Clearing Enabled and a lockout both end the user's open sessions and cancel any unused sign-in links. Each real change is written to the audit log. A save that changes no flag writes nothing. See Account Security.
Users linked to Active Directory
When Active Directory sign-in is on, a user can be linked to an AD account. The set-up is on the page Active Directory Setup. This part shows what changes in the Users screen.
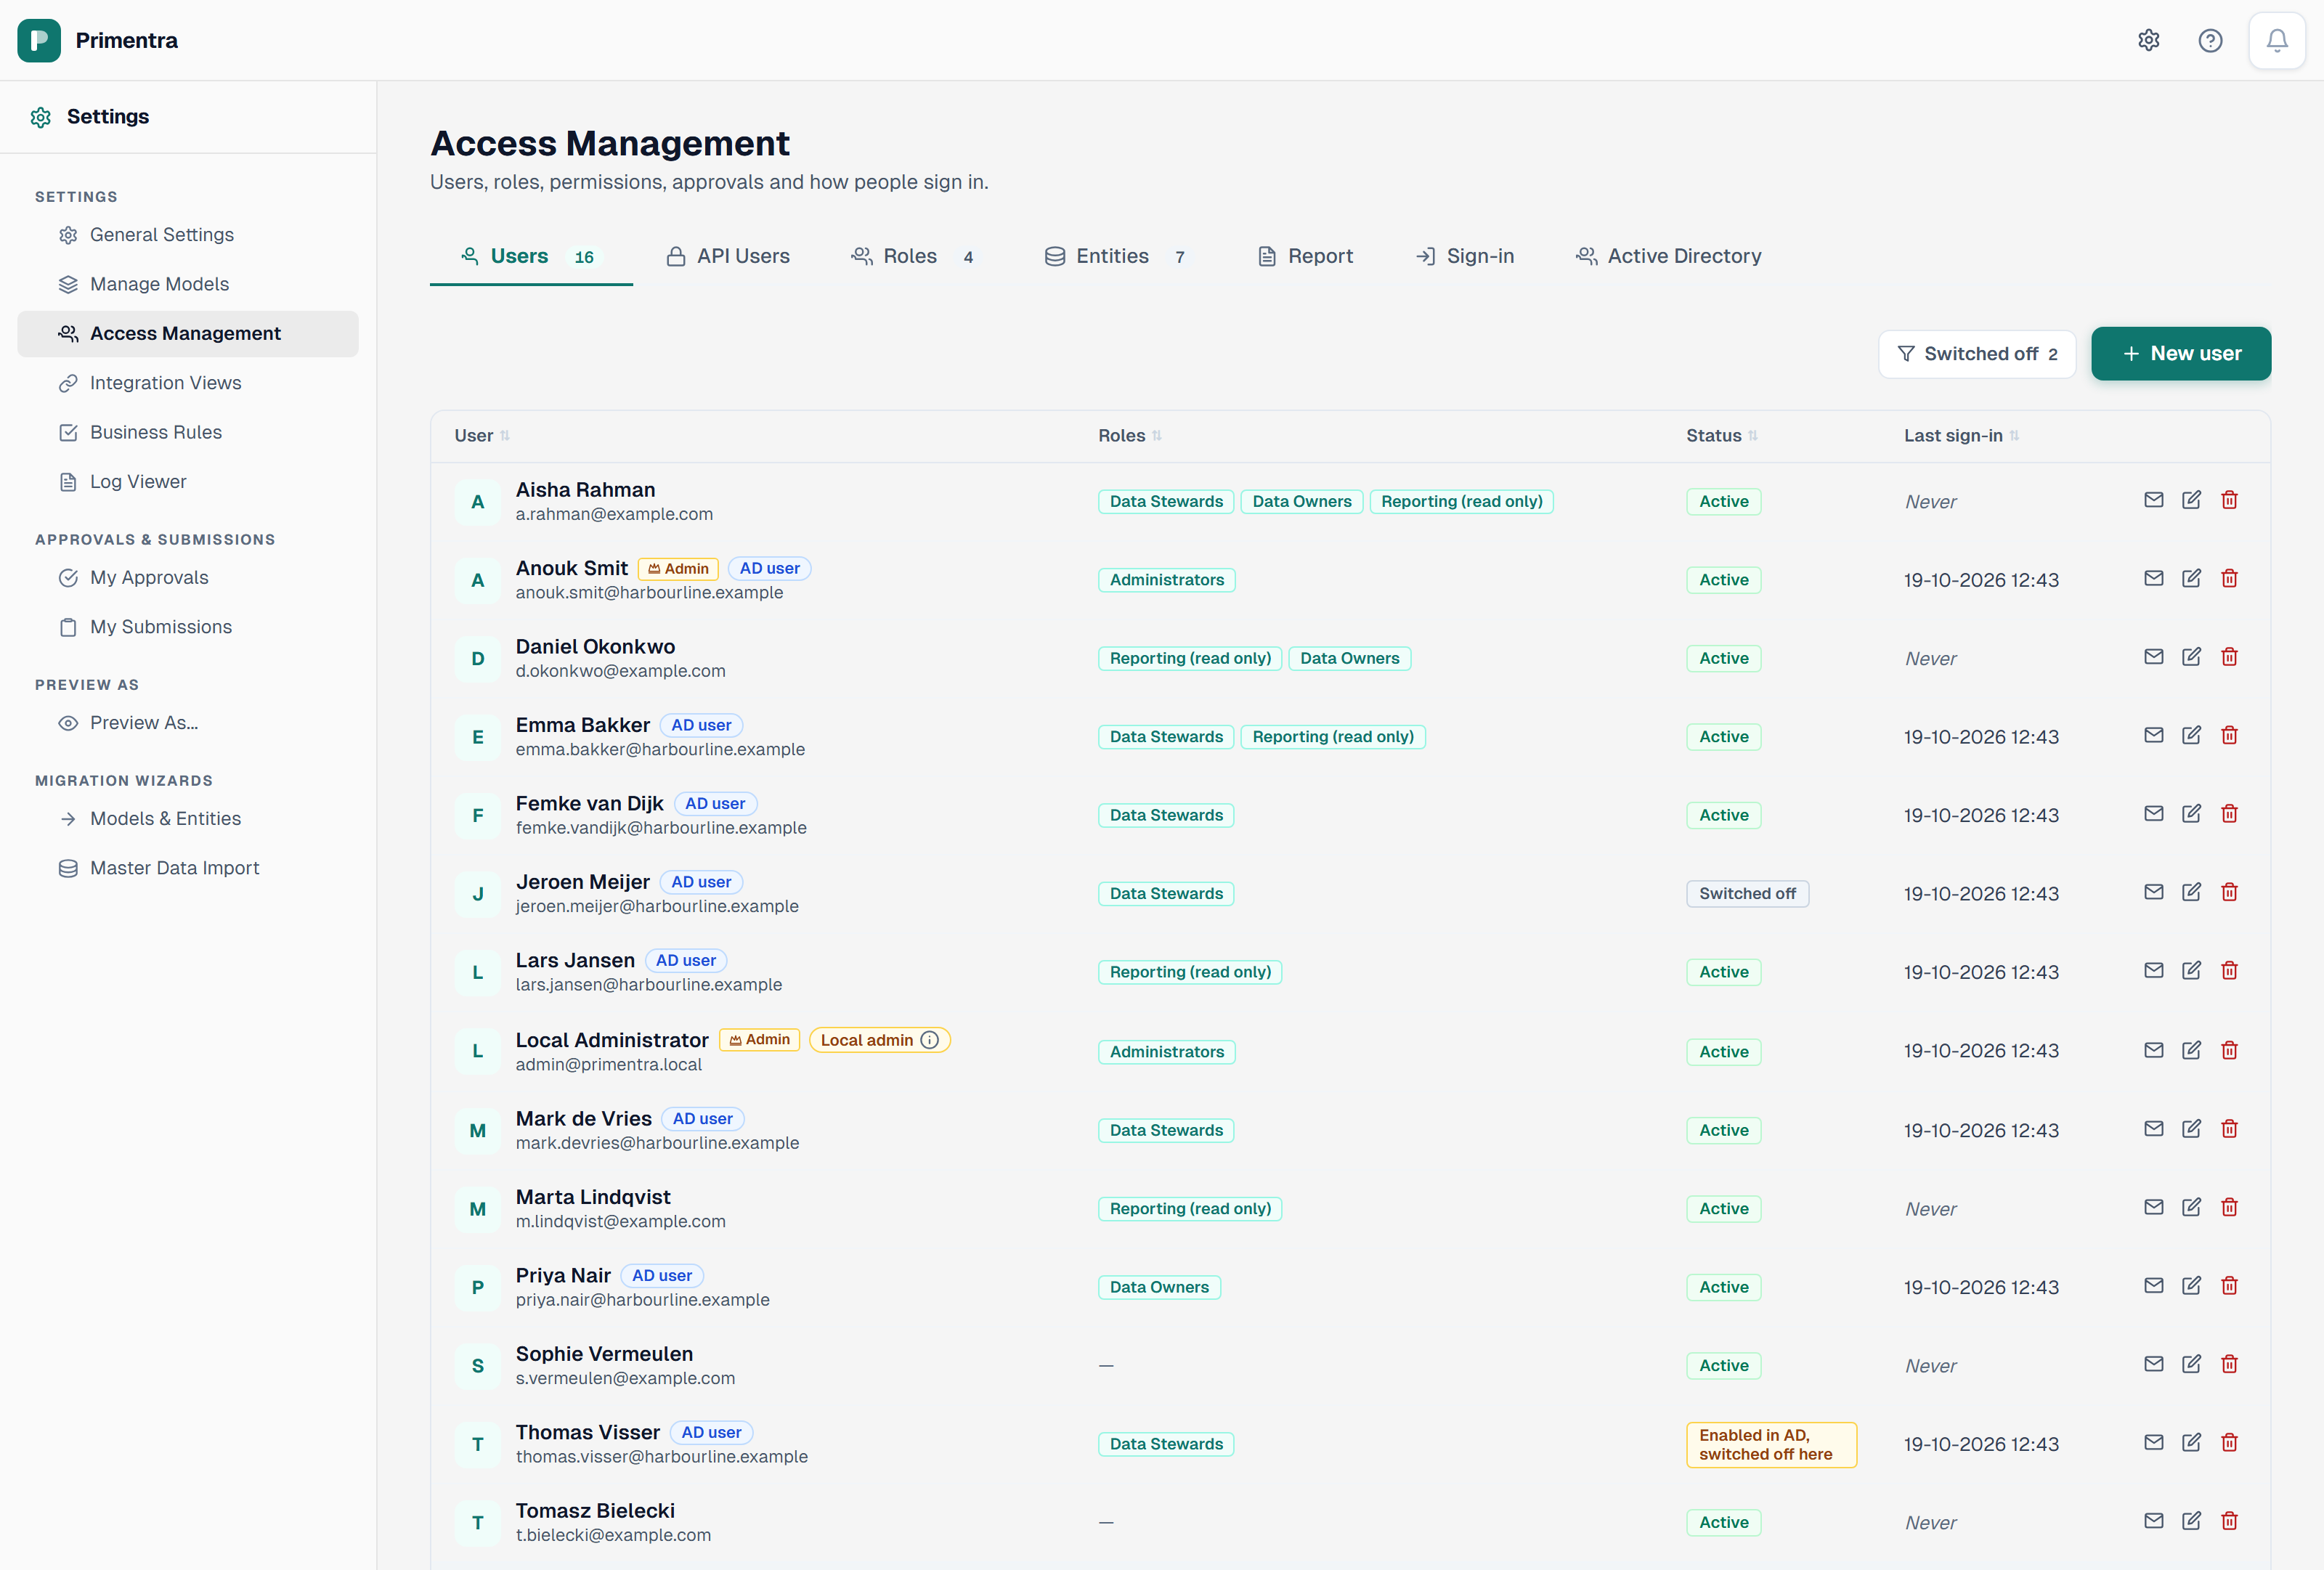
- The blue AD badge marks a linked user. Point at it to see the AD account.
- The name and email come from AD. They are read-only in the form and refresh at each sign-in.
- When the email in AD is not the one stored here, the badge Email differs in AD appears. The person can still sign in. The badge disappears after the person's next sign-in, not before.
- A role that comes from an AD group shows an AD badge. It is ticked and locked, and it disappears when the person leaves the group. Roles that you tick by hand stay.
- A user that Primentra created at the first AD sign-in has no password. The form says (no password set). Type a password only if the person must also sign in with a Primentra password.
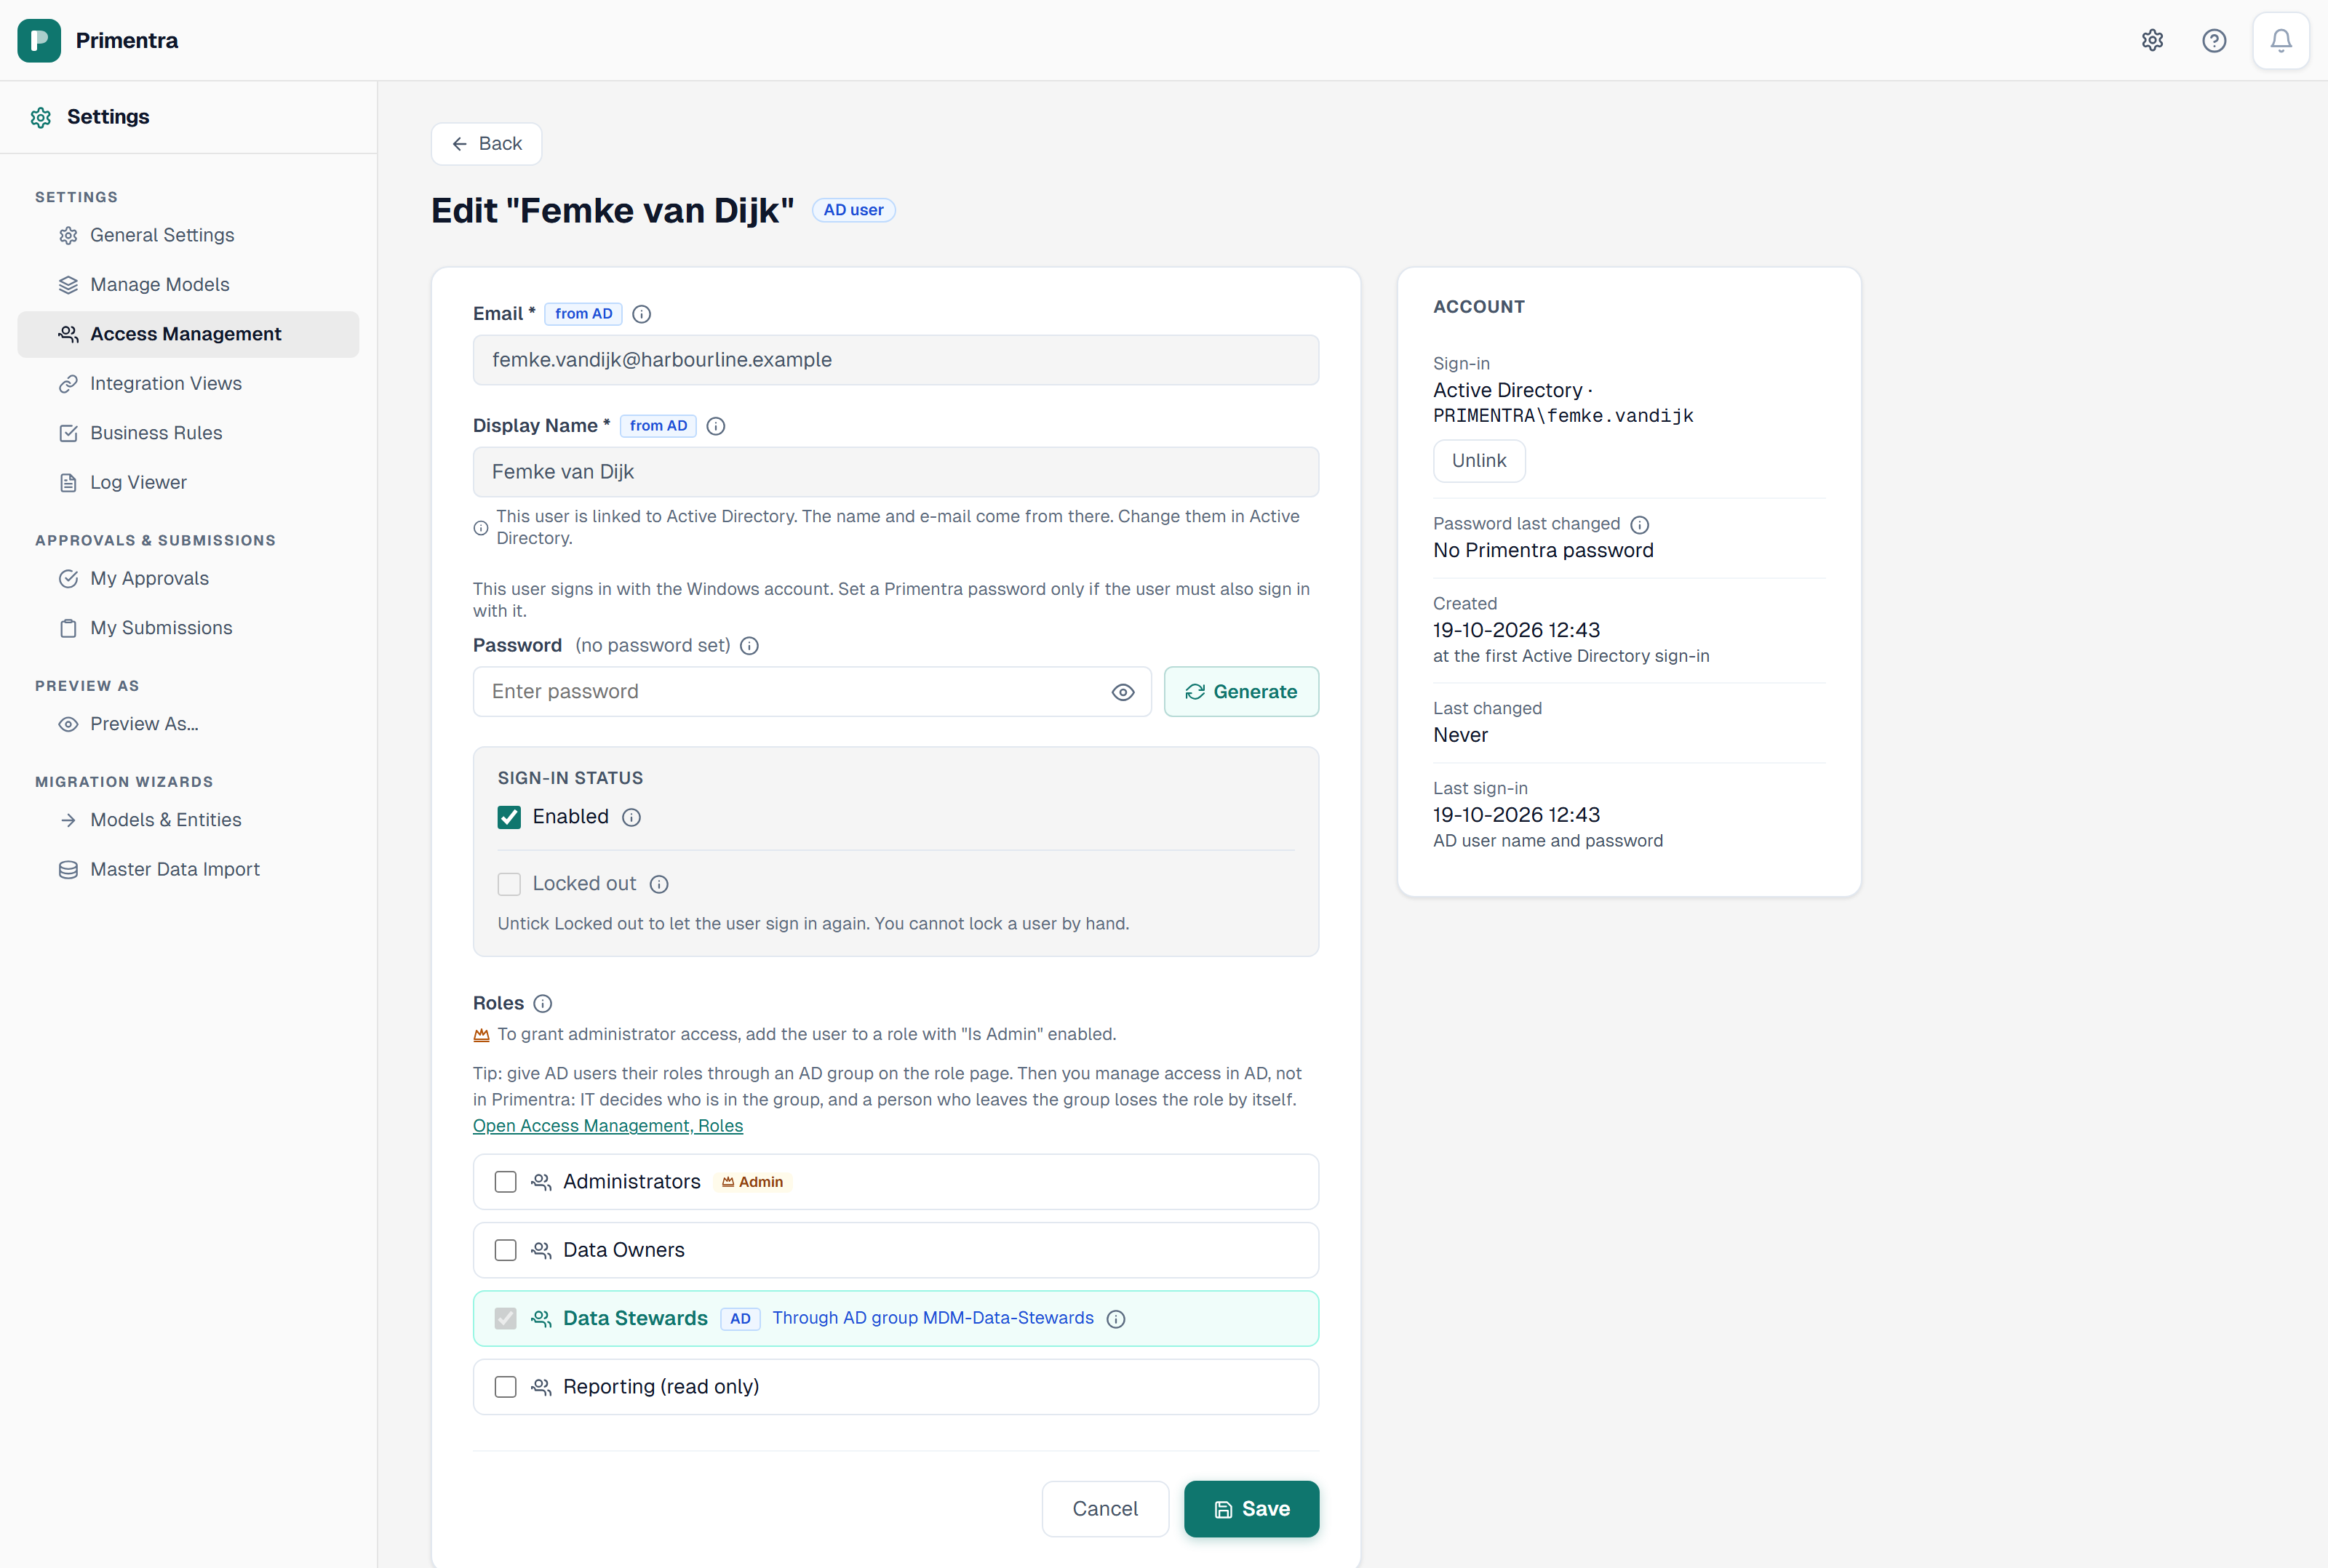
Link a user to an AD account
- Open the user.
- In the Account panel, on the Sign-in line, click Link to AD account.
- Search by name, user name or email. Type two letters or more.
- Click the person, then click Link.
Primentra copies the name and email from AD at once. If another user already has that email, the old email stays and the screen names that other user. Change or remove the other user's address, and the next sign-in copies the new one.
When you link, Primentra also reads the person's AD groups and gives the roles of those groups at once. A role that the user already has by hand and that an AD group also gives becomes a role from AD: it goes when the person leaves that group. Other hand-given roles stay as they are. If AD cannot be read when you link, the roles follow at the next sign-in or AD check, and the hand-given roles stay hand-given.
Unlink removes the link. The user keeps the account and all roles. Roles that came from AD groups become hand-given, so they no longer follow AD. Remove them by hand if the person must lose them. The name and email can be edited again.
Link and Unlink work at once, and they end the user's open sessions. Save or cancel your other changes first. The buttons stay off while the form has unsaved changes.
Primentra never links an administrator, approver or moderator on its own at the first sign-in. Link these accounts here.
Users that AD switched off
AD switches a user off when the account is disabled, expired or deleted in AD. The list shows the badge Switched off on that user.
AD never switches a user on again. When AD says the account is fine again, the user stays off until an administrator ticks Enabled in the form. The same is true for a lock.
Two things help you find these users:
- The badge Enabled in AD, switched off here marks a user that the last AD check found enabled in AD but off here. The badge disappears when you tick Enabled.
- The filter Switched off, next to New user, shows only the users that are off. It also shows how many there are.
The badge comes from the last daily check or Run now. Before the first check you see plain Switched off.
Delete a user
Deleting is a soft delete:
- The account is marked deleted and set to inactive.
- Role memberships, favorites, hidden entities, and personal settings are removed permanently.
- Audit log entries stay, so the history of what the user did remains readable.
- The email address becomes free again, because the uniqueness rule only covers accounts that are not deleted.
Deleting a linked user does not touch the account in Active Directory. The person can sign in again only after you create the user again with the same email.
Primentra refuses any change that would leave the installation without an active administrator. Deleting the last administrator returns an error instead.
Accounts Primentra creates itself
Two account types appear in the list that nobody created by hand. Both carry a blue badge.
| Badge | Account | Why it exists |
|---|---|---|
| System | system@mds-import | Created during database setup. Primentra records its own work under this name: scheduled staging runs and MDS migration imports. It cannot be deleted. |
| API | api-…@api.internal | Created with each API user. Calls made with that key are traceable in the audit log. Manage it under Administration › API Users. |
Neither account has a password, so neither can sign in. The email addresses are internal identifiers — no mail is ever sent to them.
Related
- Roles & Permissions: what each role may see and edit
- Authentication: how users sign in
- Account Security: lockout and password rules
- Active Directory & SSO: sign in with a Windows account
- REST API: API users and keys
Did not find what you need?
Try the troubleshooting pages, or ask us.